Johns Hopkins Bayview Medical Center is notifying more than 3,100 patients that their personal and medical information may have been exposed after an employee uploaded a spreadsheet containing patient data to an unauthorized artificial intelligence (AI) platform.
According to Johns Hopkins, the incident was discovered during an internal review. The employee reportedly uploaded the spreadsheet to a public, third-party AI tool that had not been approved for institutional use.
The spreadsheet contained information related to patient admissions and treatment between May and September 2026. The medical center said the incident involved information that could identify patients and provide details about their medical care.
What Information May Have Been Exposed?
The spreadsheet may have included several types of patient information, including names, admission and treatment dates, medical record numbers, account numbers, departments of service, medications administered and the names of healthcare providers.
Johns Hopkins said the spreadsheet did not contain Social Security numbers, financial account information or other identifying information, according to the information provided by the medical center.
The extent to which the uploaded information may have been accessed or retained by the AI platform was not specified in the provided details.
Medical Center Investigates Unauthorized AI Upload
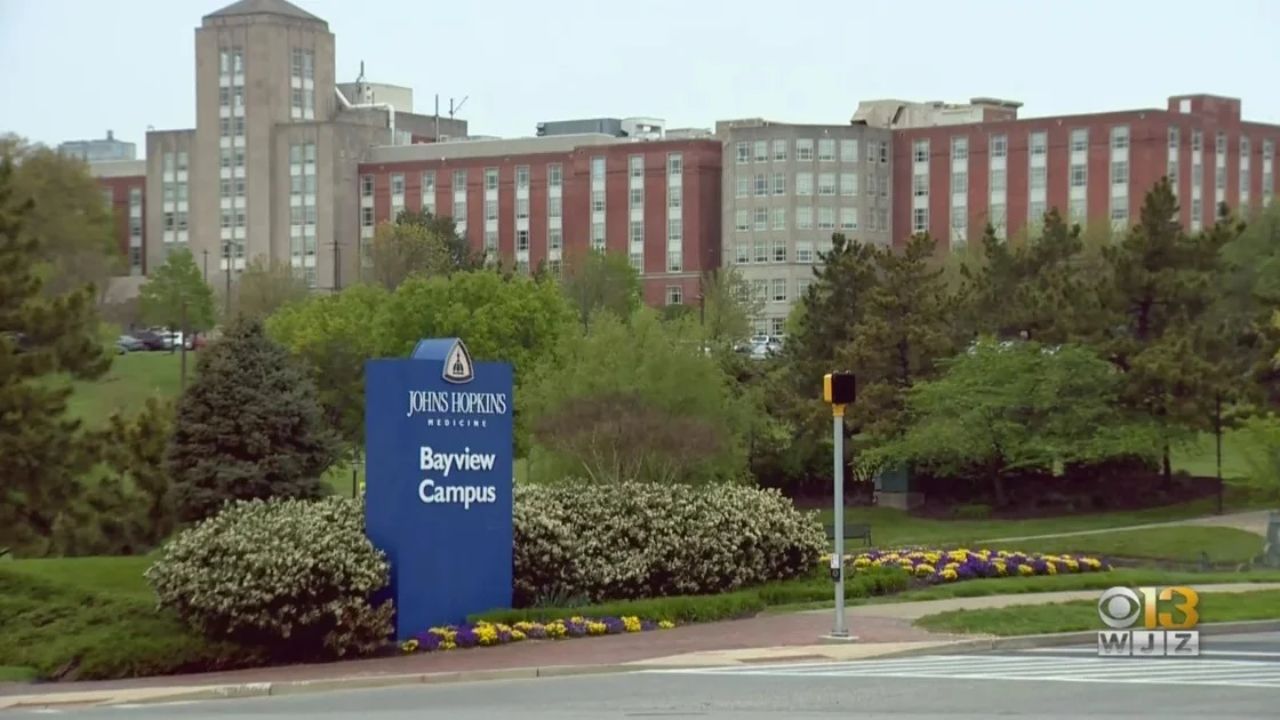
After discovering the incident, Johns Hopkins Bayview Medical Center (JHBMC) launched an investigation and took steps to address the unauthorized disclosure.
The medical center directed the employee to delete the original AI prompt, the subsequent conversation thread and the uploaded document from the platform’s history. It also contacted the company operating the AI service and requested that the information be deleted.
Johns Hopkins said it implemented corrective measures intended to reduce the risk of similar incidents in the future.
Those measures included reinforcing policies and training related to protected health information, emphasizing restrictions on unauthorized applications and AI tools, and providing additional education about institutionally approved tools.
The incident highlights the importance of following data protection policies when using AI services in healthcare settings, where spreadsheets and other digital records can contain sensitive patient information.
Patients to Receive Notification Letters and Credit Monitoring
On October 22, Johns Hopkins Bayview Medical Center began mailing notification letters to patients whose information was identified during its review.
The letters include instructions for enrolling in 12 months of complimentary credit monitoring through Experian IdentityWorks.
Patients who receive a notification letter should review the instructions carefully and follow the enrollment steps provided if they wish to use the offered service.
JHBMC has also established a toll-free call center to answer questions about the incident and the notification process.
Patients can contact the call center at 1-833-931-7766, Monday through Friday, from 9 a.m. to 9 p.m. Callers should reference engagement number B174716.
Patients who believe they may be affected can use the contact information to seek clarification about the incident and the available assistance.
Johns Hopkins Responds to the Incident
Johns Hopkins said it takes the privacy and security of patient information seriously and regrets the concern the incident may cause.
“Johns Hopkins is committed to maintaining the privacy and security of its patients’ information and is taking this incident very seriously,” the medical center said. “We sincerely regret any inconvenience or concern this may have caused.”
The medical center’s investigation and corrective measures are intended to address the disclosure and strengthen safeguards surrounding the use of AI tools and the handling of protected health information.
For affected patients, the notification letters and the dedicated call center provide the primary channels for learning more about the incident and accessing the complimentary credit monitoring offer.
